Day two of VMware Explore on Tour in Frankfurt is about to start, so let me quickly look back at day one. With a coffee, of course. After almost twenty years of VMware events, some habits never change.
Let me start with the elephant in the room. When I talk with customers, the mood around VMware is not always relaxed. Licenses changed, renewals got more expensive, and the question I hear most is simple: “Are we still on the right platform?” I understand that question. But I also see that many customers already own much more than they use today. So that was my lens for day one: not only what’s new, but what customers can get out of what they already pay for.
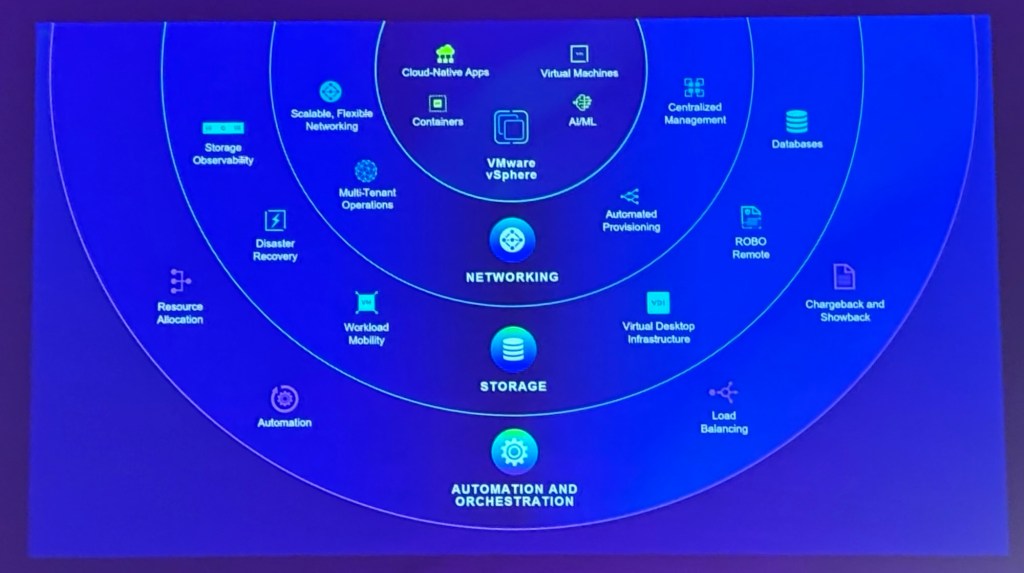
The slide that stuck with me was a simple one. vSphere in the middle, with networking, storage, and automation and orchestration as rings around it. Every customer sits somewhere else on that picture, and that’s exactly where the value conversation starts.
The hypervisor gets an armor
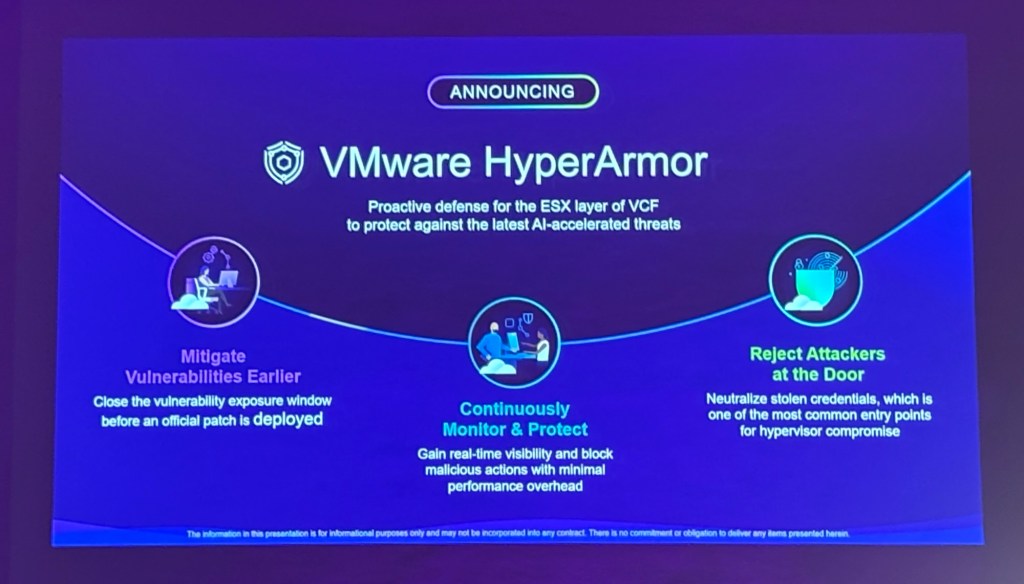
Security was the big story of the keynote. VMware HyperArmor brings proactive defense to the ESX layer itself. It helps close the window between a vulnerability and the patch, watches what happens on the host, and stops attackers who come in with stolen credentials. Add vDefend, which was also announced for VVF on stage, and reports that Broadcom moves to monthly security updates, and the message is clear: the hypervisor is a target, and it gets treated like one.
A second life for your servers
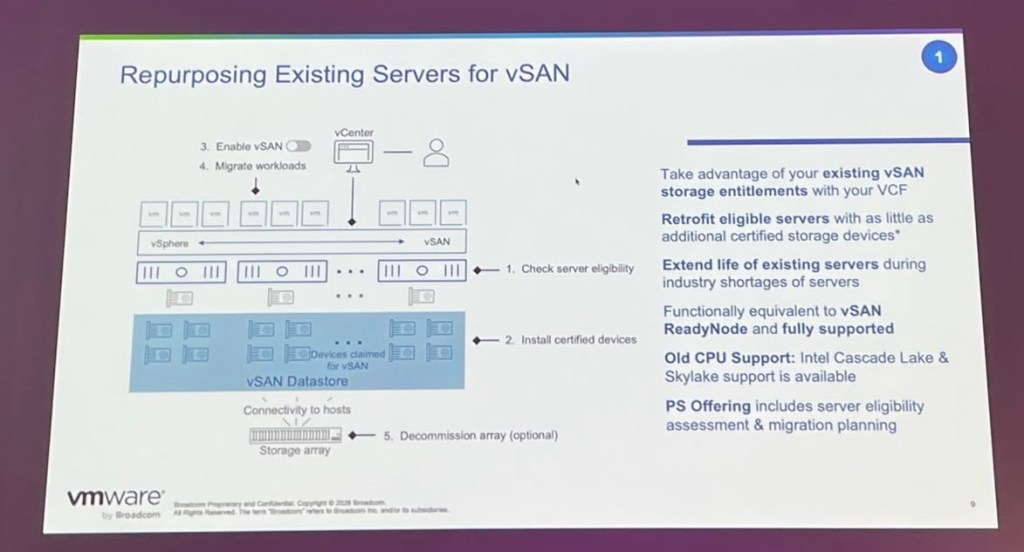
Storage got my attention too. One session showed how to repurpose existing servers for vSAN, using the vSAN entitlement that already comes with VCF. Add certified disks, check eligibility, and older Cascade Lake and Skylake servers get a second life. With today’s server shortages, that’s not a bad idea. And yes, as a NetApp A-Team member I smiled at the “4-in-1 storage” slide. Not every array disappears tomorrow, but doing the math is never a bad idea.
Cyber recovery is not disaster recovery
My favourite session was the disaster recovery deep dive. The key message: cyber recovery is not the same as disaster recovery. With a disaster you fail over to your latest copy and follow your runbook. With ransomware you recover in an isolated clean room, test multiple recovery points and work your way back to a known good state. W&W Gruppe shared how they replicate many workload domains to one recovery site, including a small gotcha about site IDs. That’s the kind of lesson you only get from people who have actually done it.
And of course, AI
The Private AI Cloud stack and Tanzu with governed agents show where Broadcom is heading. Most of my customers are not there yet, but one question comes up more and more: “Where will our AI run, and who controls the data?”
A special day for ITQ
For ITQ it was a special day as well. We are one of the Signature Sponsors, and we use Explore on Tour to launch the ITQ Cloud Platform, our own cloud built on VMware Cloud Foundation.
Today is day two, and I’m curious what the sessions and the hallway talks will bring. I’ll keep you posted.
Are you in Frankfurt? Come say hi, I’m always up for a coffee. Not here, but wondering how to get more value from your VMware investment? Send me a message, I’m happy to think along.


Leave a Reply